Master Penetration Testing
A methodology-driven penetration testing course that teaches you to plan, execute and report professional security assessments across networks and applications.
Start Learning
Join learners who transformed their careers with MITS Edge.
Program Overview
Penetration Testing is an advanced-level live online course running 10 weeks (72 hrs), priced at $800 USD, taught by instructors in evening and weekend cohorts for learners in the US and Canada, with a certificate of completion.
A methodology-driven penetration testing course that teaches you to plan, execute and report professional security assessments across networks and applications. What you will build: a scoped penetration test of a simulated company network with a client-ready report. Tools and technologies: Kali Linux, Nmap, Metasploit, Burp Suite, Nessus (Essentials), Cobalt Strike concepts, Python. Format: 72 hours of live, instructor-led online training over about 10 weeks, in evening and weekend cohorts for learners in the US and Canada, with hands-on labs, recorded sessions and mentor support. Career pathways: Penetration Tester, Security Consultant (junior), Vulnerability Assessment Analyst, Red Team Associate. Resume review and interview guidance are available to all learners.
Course Highlights
- 72 hours of live instructor-led training
- Hands-on projects and real-world labs
- Tools: Kali Linux, Nmap, Metasploit
- Certificate of completion
- Career guidance for US & Canada job market
- Recorded sessions and mentor support
Minimum Requirements
- Networking, Linux and basic security knowledge
- Laptop or desktop with stable internet
Who is this for ?
- Security professionals formalising pentest skills
- Analysts transitioning to consulting roles
- Learners preparing for pentest certifications
Curriculum
Course Curriculum
5 modules · 17 topics0 hours total
- 1Scoping
- 2rules of engagement
- 3contracts and legal aspects
- 4threat modelling
Industry-Recognized
Certification
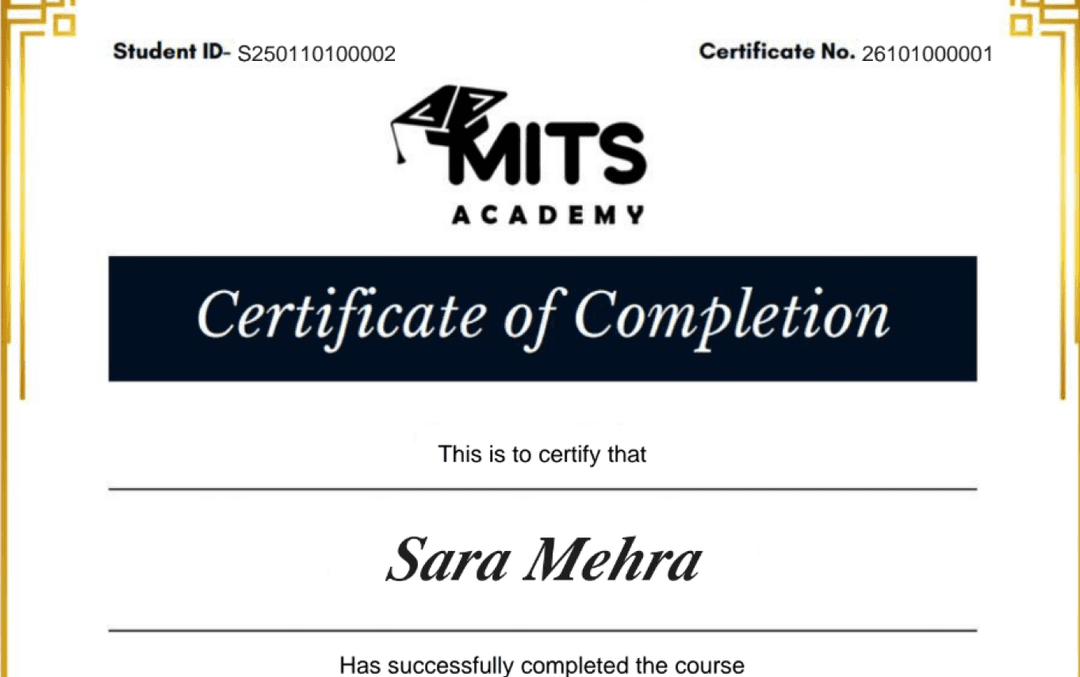
Upon successful completion, you receive a certificate of completion for the Penetration Testing program that you can share with employers and add to your LinkedIn profile — a record of the hands-on skills and projects you completed.
- Verifiable ID: Unique credential link for LinkedIn.
- Skill Validation: Proof of hands-on project completion.
- Corporate Branding: CO-branded with your company logo.
Student Reviews
Why learn this online
Cybersecurity has a persistent, well-documented shortage of qualified professionals, which keeps demand high for motivated newcomers. Learning online through live sessions and hands-on labs lets you build networking and security fundamentals, practice with real tools, and work toward CompTIA Security+ — the combination that opens entry-level SOC analyst roles.
Who this is for
- ✓Detail-oriented, process-driven learners
- ✓IT professionals moving into security
- ✓Career switchers from compliance or audit
Career outcomes
- Security Analyst
- SOC Analyst
- Information Security Associate
- GRC Analyst
Frequently asked questions
How much does the Penetration Testing course cost?
The Penetration Testing course costs $800 (USD) for 10 Weeks (72 hrs) of live, instructor-led online training. The fee covers live classes, recorded sessions, hands-on projects, mentor support and the certificate of completion.
What projects will I build in Penetration Testing?
You will build a scoped penetration test of a simulated company network with a client-ready report.
Which tools and technologies does Penetration Testing cover?
Penetration Testing covers Kali Linux, Nmap, Metasploit, Burp Suite, Nessus (Essentials), Cobalt Strike concepts, Python.
Is the Penetration Testing course online or in person?
The Penetration Testing program is delivered live and online with instructor-led sessions, so you can join from anywhere in the US, Canada, or beyond. Sessions are interactive and recordings are available for review.
How long is the Penetration Testing course?
The Penetration Testing program runs for 10 Weeks (72 hrs). Cohorts are scheduled in the evenings and on weekends to fit around a full-time job.
What level is the Penetration Testing course — is it suitable for beginners?
The Penetration Testing program is pitched at a advanced level. Some prior familiarity helps, and the curriculum builds toward job-ready skills.
Do I get a certificate after completing Penetration Testing?
Yes — you receive a verifiable certificate of completion for the Penetration Testing program, which you can share with employers and add to your LinkedIn profile.
Does the Penetration Testing course include placement or career support?
Yes. MITS Edge programs include career support — resume reviews, mock interviews, and job-search guidance aligned to the US and Canadian hiring markets.
Do I need any prior experience to join Penetration Testing?
Recommended prerequisites: Networking, Linux and basic security knowledge; Laptop or desktop with stable internet.
Can I get into cybersecurity without experience?
Yes. Many enter through an adjacent IT role or by building a strong lab portfolio. A SOC analyst position is the most common entry point.
What certification matters most for security?
CompTIA Security+ is the most widely recognized entry credential, with Network+ helpful first if you are new to IT.
Related Courses
Cyber Security – Career Program
A six-month cybersecurity career track covering networking, defensive security, SOC operations, ethical hacking and cloud security, with certification-aligned labs and a final incident-response capstone.
Ethical Hacking – Essential
An accessible introduction to ethical hacking — how attackers think, the phases of a penetration test and the core tools — practised only in isolated, legal lab environments.
Cyber Security Fundamentals
Learn the core concepts of cybersecurity — threats, controls, networks, identity and risk — a practical foundation for any security, IT or compliance career.
Ethical Hacking Course
A lab-intensive ethical hacking course covering the full penetration-testing lifecycle — from enumeration and exploitation to privilege escalation and reporting — on intentionally vulnerable systems.